Google dismantles network that infected millions of Android devices with factory-installed malware
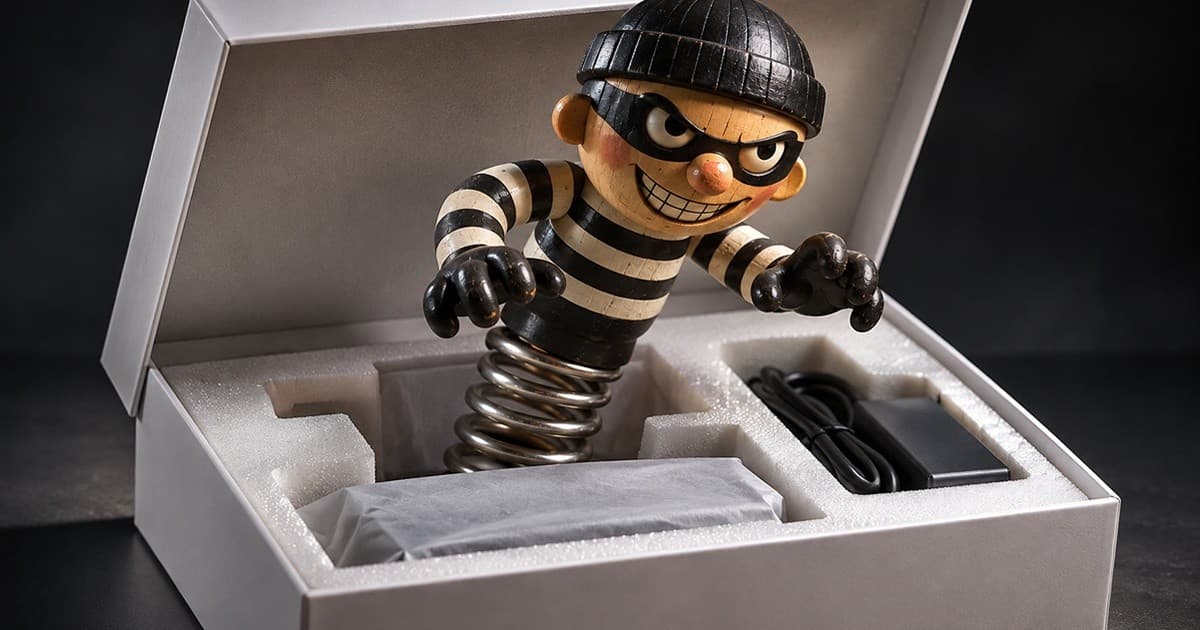
Google disclosed in early November that it dismantled a global criminal network that infected millions of Android devices, including streaming TV Boxes, telemedicine equipment, karaoke players and digital signage screens. According to the investigation, Chinese manufacturer Videostrong deliberately embedded malicious software in some devices, which arrived with a factory-installed backdoor. That access was used to build a botnet for ad fraud. Google estimated its measures could block access to another 10 million compromised devices.
In 35 seconds
- Google dismantled a criminal network that infected millions of Android devices, including streaming TV Boxes.
- Chinese manufacturer Videostrong allegedly embedded malicious software at the factory in some of its devices.
- The devices were part of a botnet used for ad fraud and to hide the origin of the operations.
Read the full story at Rosario3
IASummary generated by artificial intelligence from a story by Rosario3. It may contain errors: the original source prevails.

Comments
Be respectful. Comments reported by several people are hidden until a moderator reviews them.
You do not need an account to read, only to comment. Sign in with a code sent to your email or with your Google account. We only show the name you choose, never your email.